

Cisco Access Manager Release Notes
This page summarizes the incremental features released in Cisco Access Manager. Reference it quickly and easily using the shortcut cs.co/am-releases .
Client Certificate Attributes in Session Log Details
2026-09-14
Client certificate details used for each EAP-TLS authentication are now available under the Session Log > Details when you click on the session Status. This is helpful when you need to verify the certificate identity for EAP-TLS authentications and differentiate authorizations in Access Rules based on the available certificate attributes.
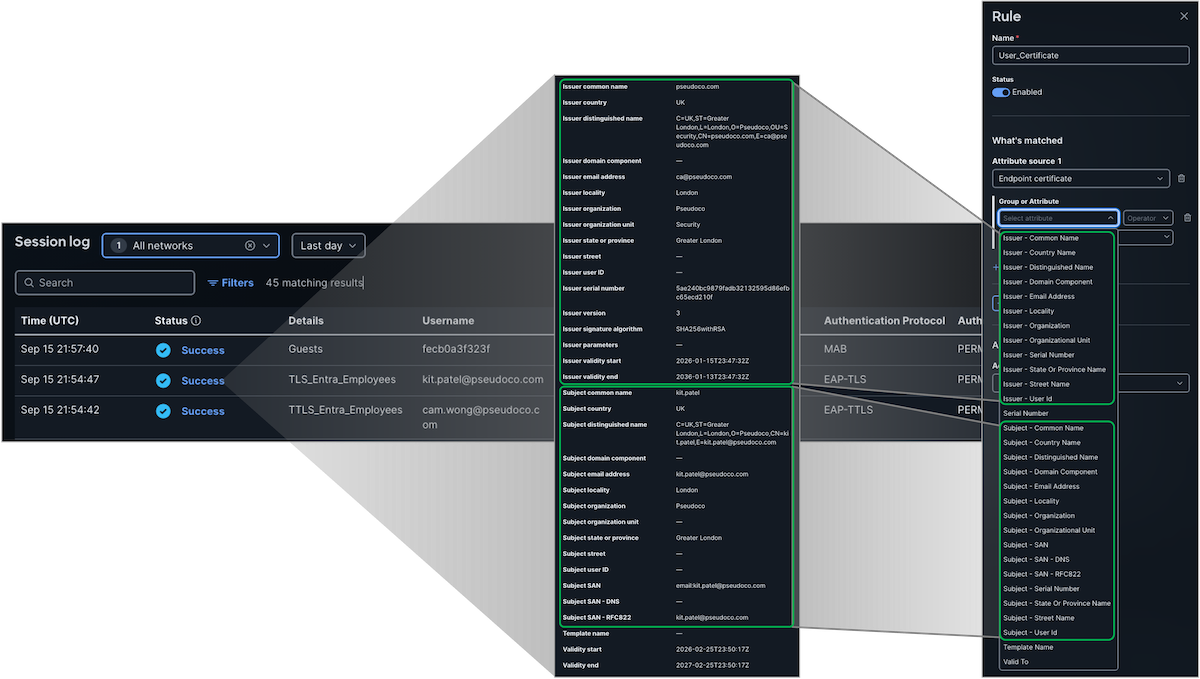
All of the following client certificate attributes are available in the Network Access Details:
|
|
|
iPSK per-Client MAC
2026-09-09
Previously, Access Manager allowed the assignment of one identity pre-shared key (iPSK) per Access Rule, shared across all clients in one or more Client Groups. This meant a compromised or decommissioned client forced an iPSK rotation for all clients. Admins may now assign a unique iPSK to individual clients and choose how individual Access Rules resolve the final PSK at authentication time.

Access Manager now offers three modes per Access Rule for Authorization:
- Client iPSK only: Only clients with a configured iPSK passphrase can authenticate against this rule. Use this to require and enforce per-MAC iPSK. Configure the per-client MAC in the Clients page.
- Client iPSK with fallback: Clients with a configured iPSK passphrase use it to authenticate; all other clients fall back to the passphrase set below. Use this when transitioning from a shared PSK for all clients to the more secure Client iPSK Only policy. Configure the per-client MAC in the Clients page.
- Override client iPSK: All clients authenticate using the passphrase set below, regardless of any per-client iPSK. Use this when all clients matching a rule all use the same PSK. This was the previous behavior where all clients matching a rule must have the rule's assigned PSK.

CRL URL Management via UI
2026-08-25
Certificate revocation lists (CRL) URL management was previously limited to the REST API with no visibility in the user interface for status or revocation health. You may now manage CRLs from the Access Manager > Configure > Certificates page to upload CRL files (*.pem), configure a CRL URL, confirm hourly CDP retrieval, enable verification, and manage base or delta CRL lifecycles to ensures automated real-time updates.

Cisco AI Assistant
2026-07-20
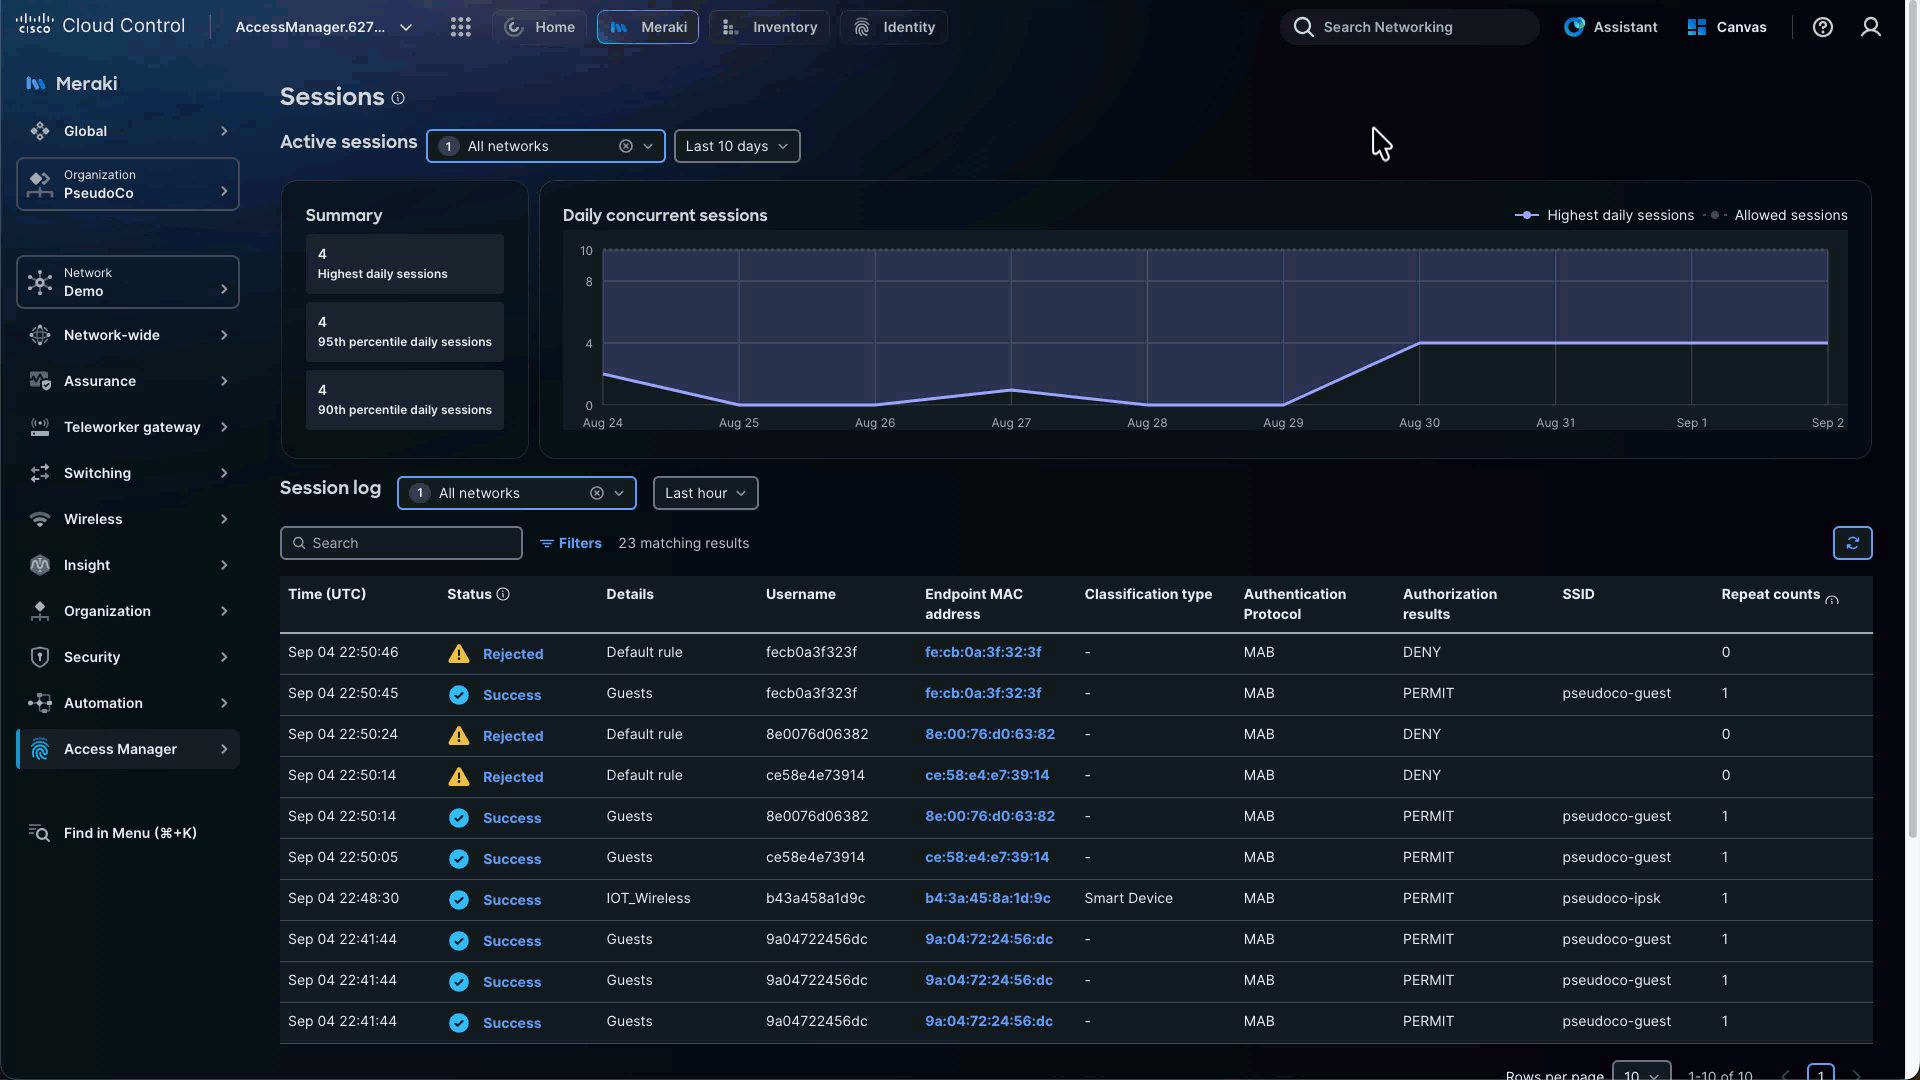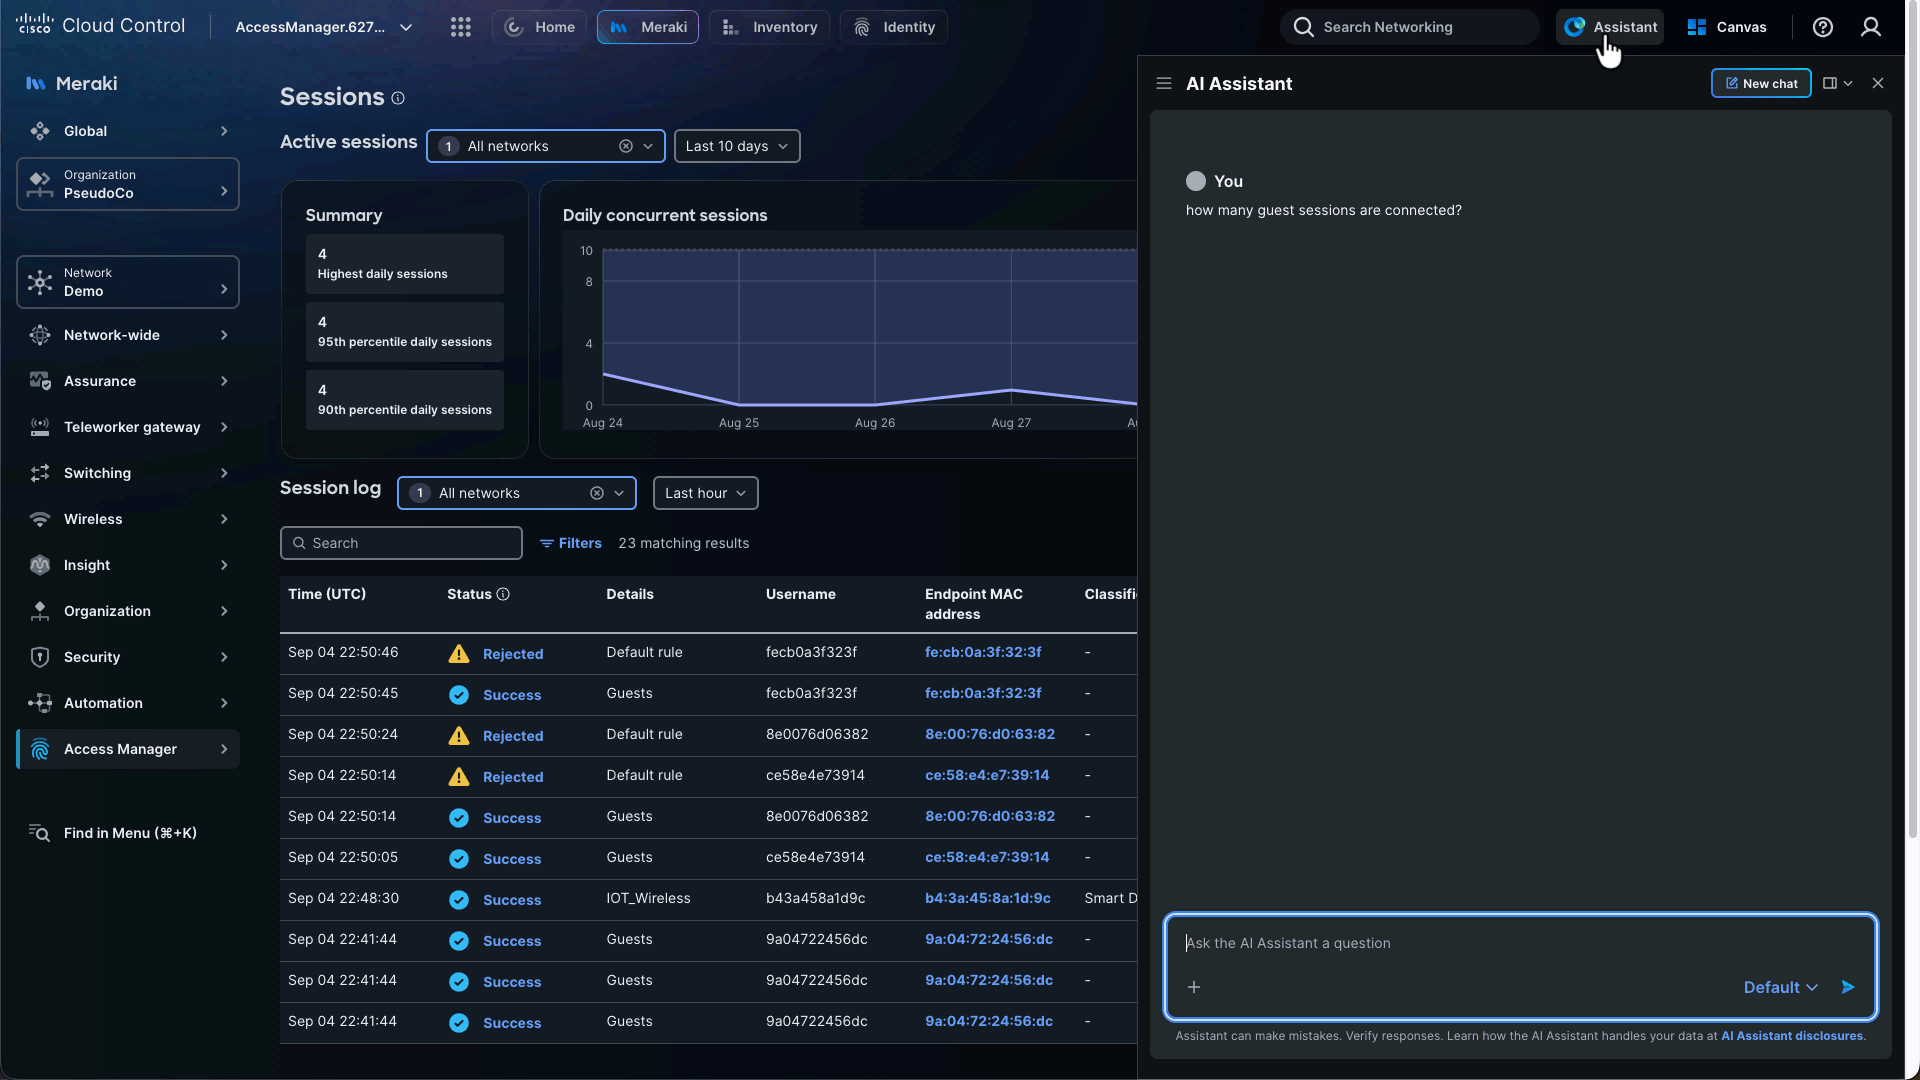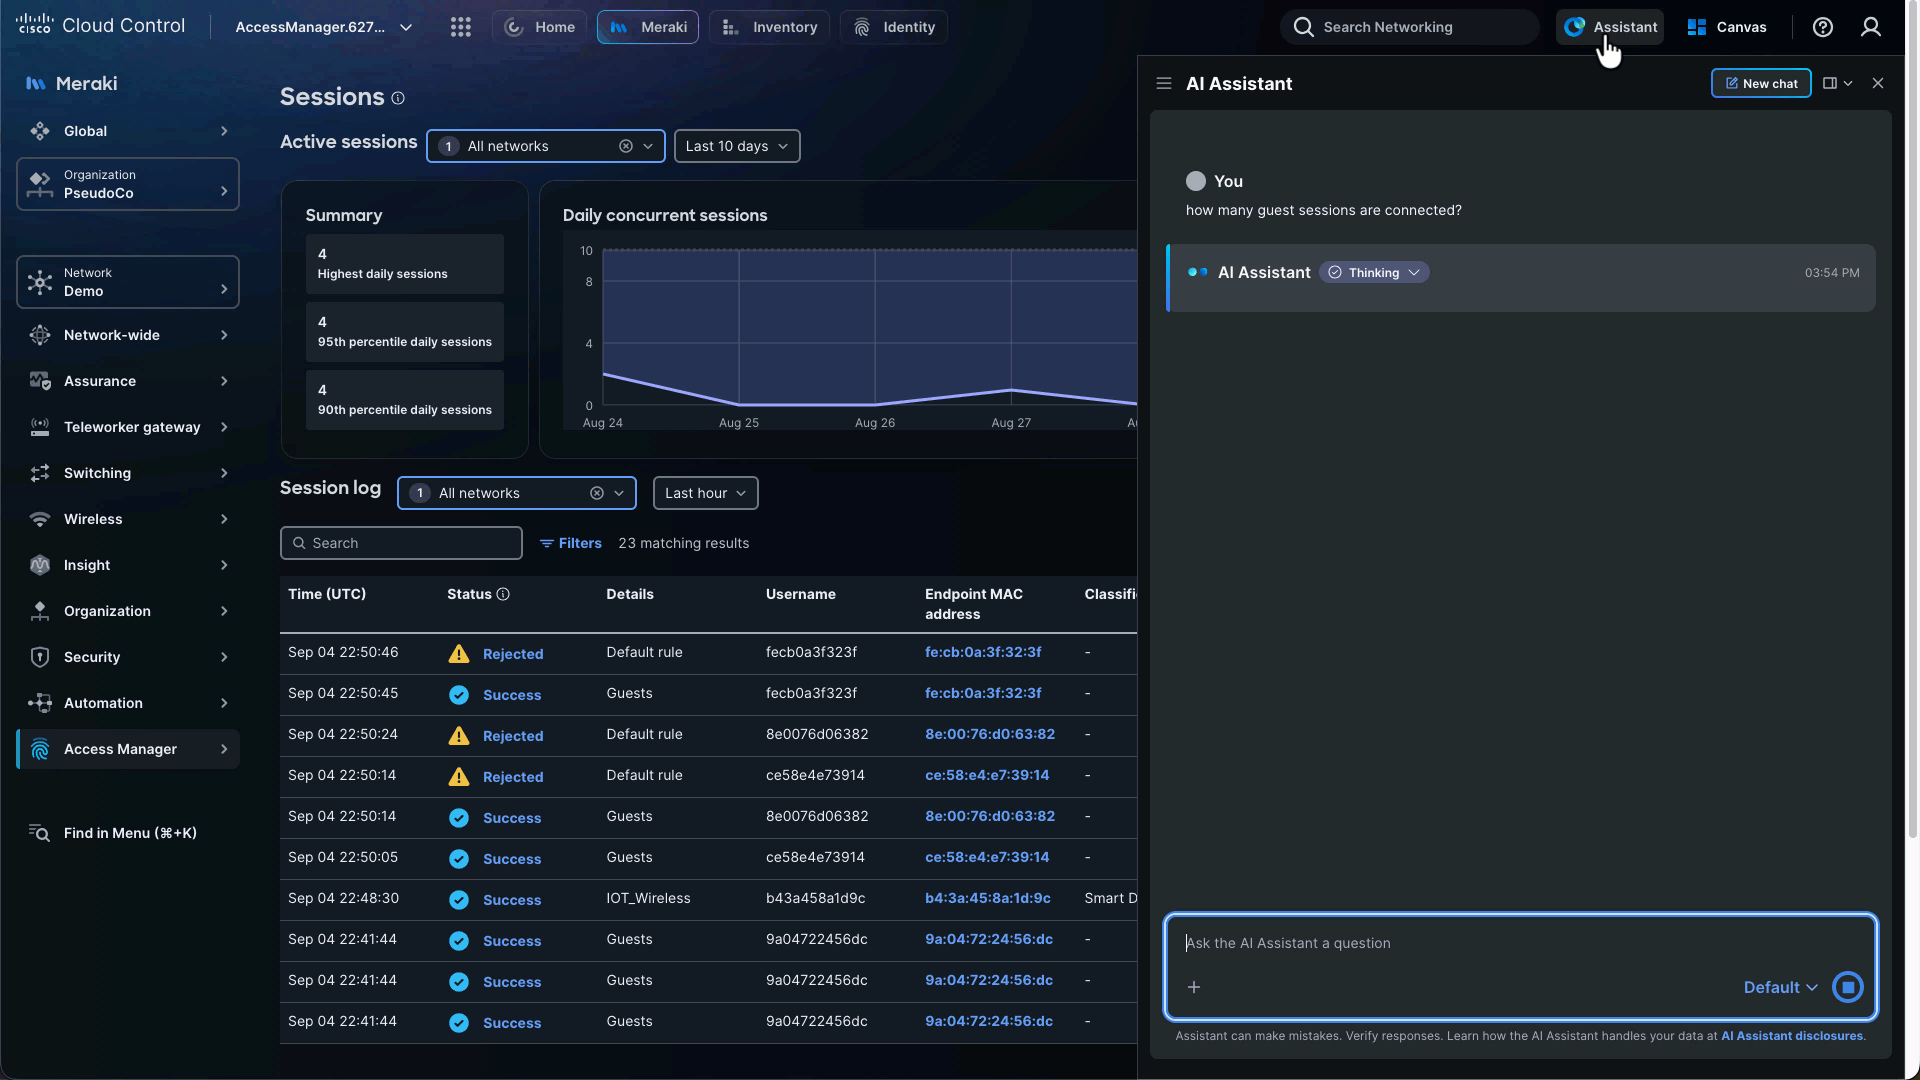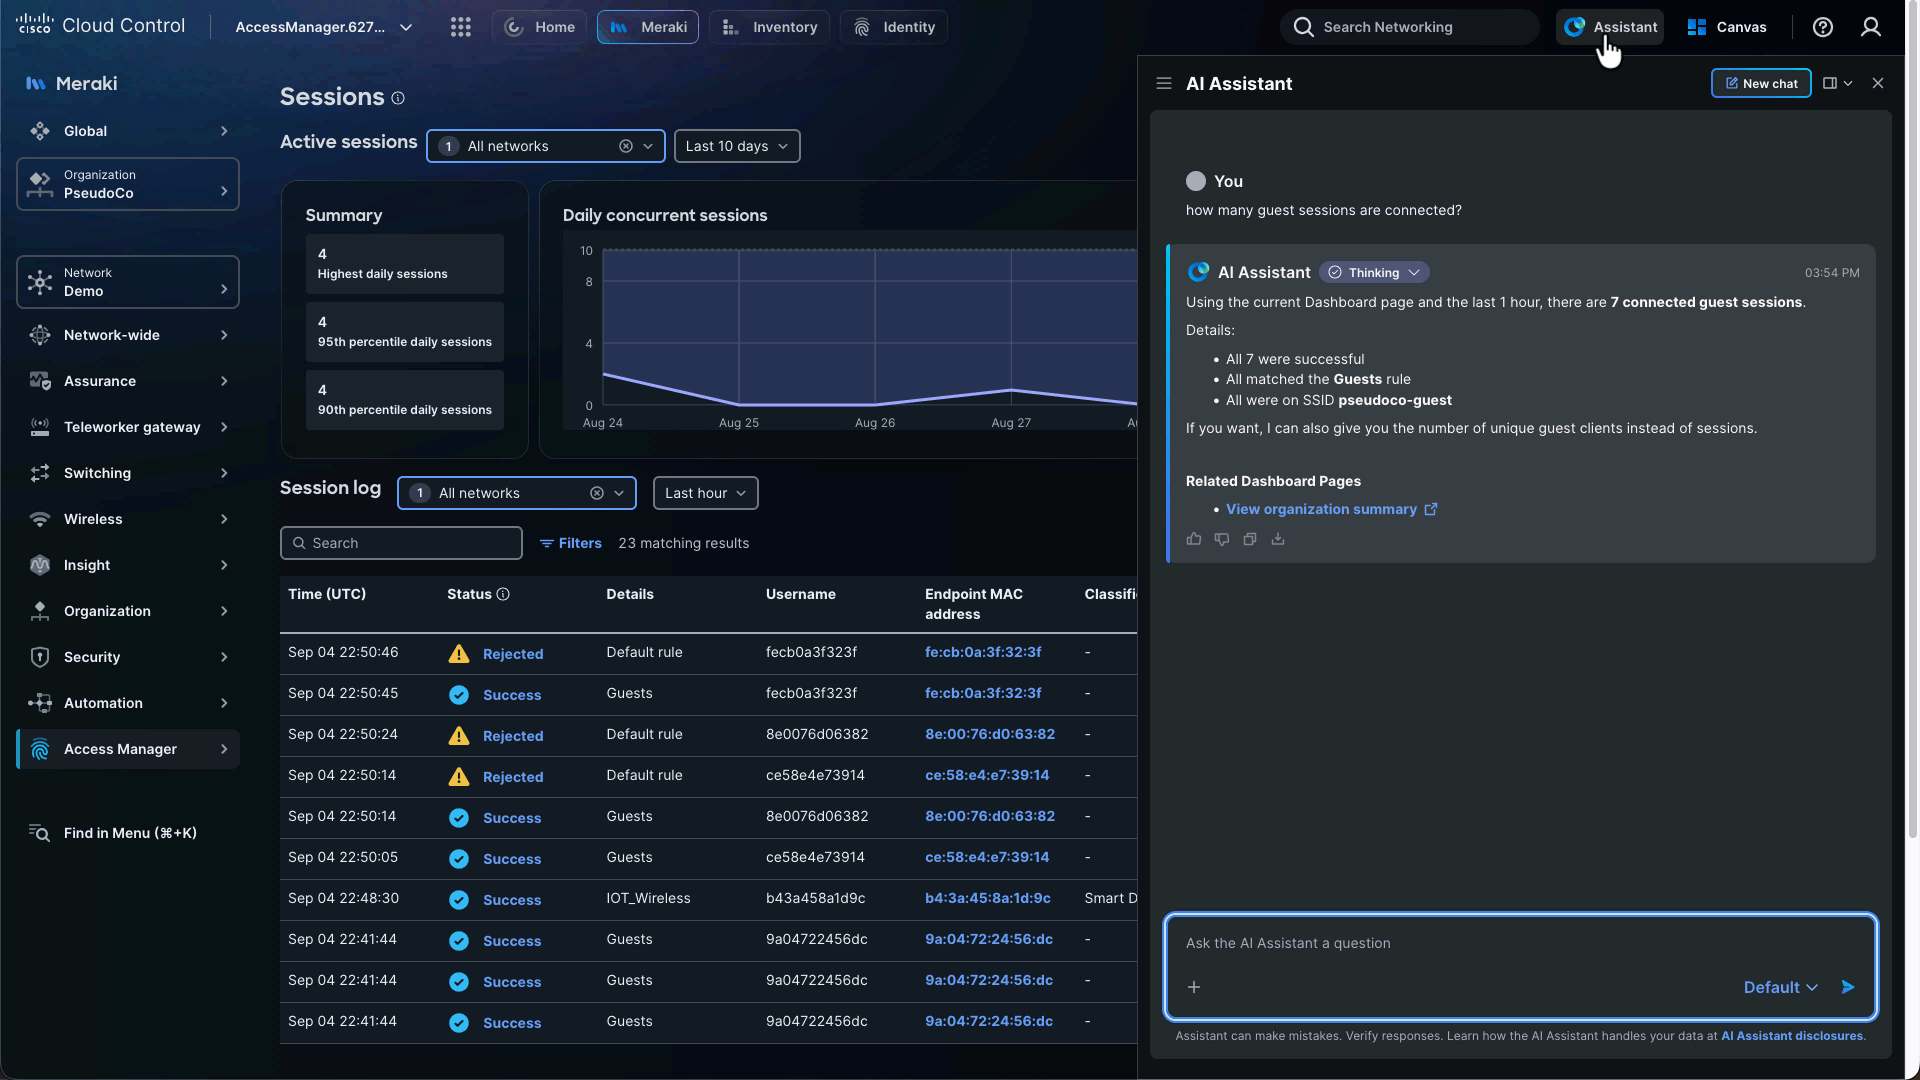
Cisco AI Assistant may be used to query (read-only) information about your Access Manager Session Logs, Policy Sets, Identity Providers, Clients, Group Policies, and Certificates within the dashboard.
Access Policies Fallback Options
2026-07-15
Additional fallback options are now supported under Switching > Configure > Access Policies :
- Disable Port Bounce
- Critical Auth VLAN (Data and Voice)
- Failed Auth VLAN
Cloud-based Profiling Generally Available
2026-07-01
Cloud-based Profiling is now generally available in all organizations.
Cloud-based Profiling Rollout
2026-05-01
Cloud-based Profiling begins a phased rollout to all organizations using observed attributes from the CDP, DHCP, and LLDP protocols with four classification labels: Type, Manufacturer, Model, OS. The rollout to all organizations will occur over the next 2 months. To view these classification labels, go to Access Manager > Configure > Clients, select the ⛭ then enable the respective attribute columns.

Use the Clients page's Filters option to view all client endpoints with the same profiling labels:
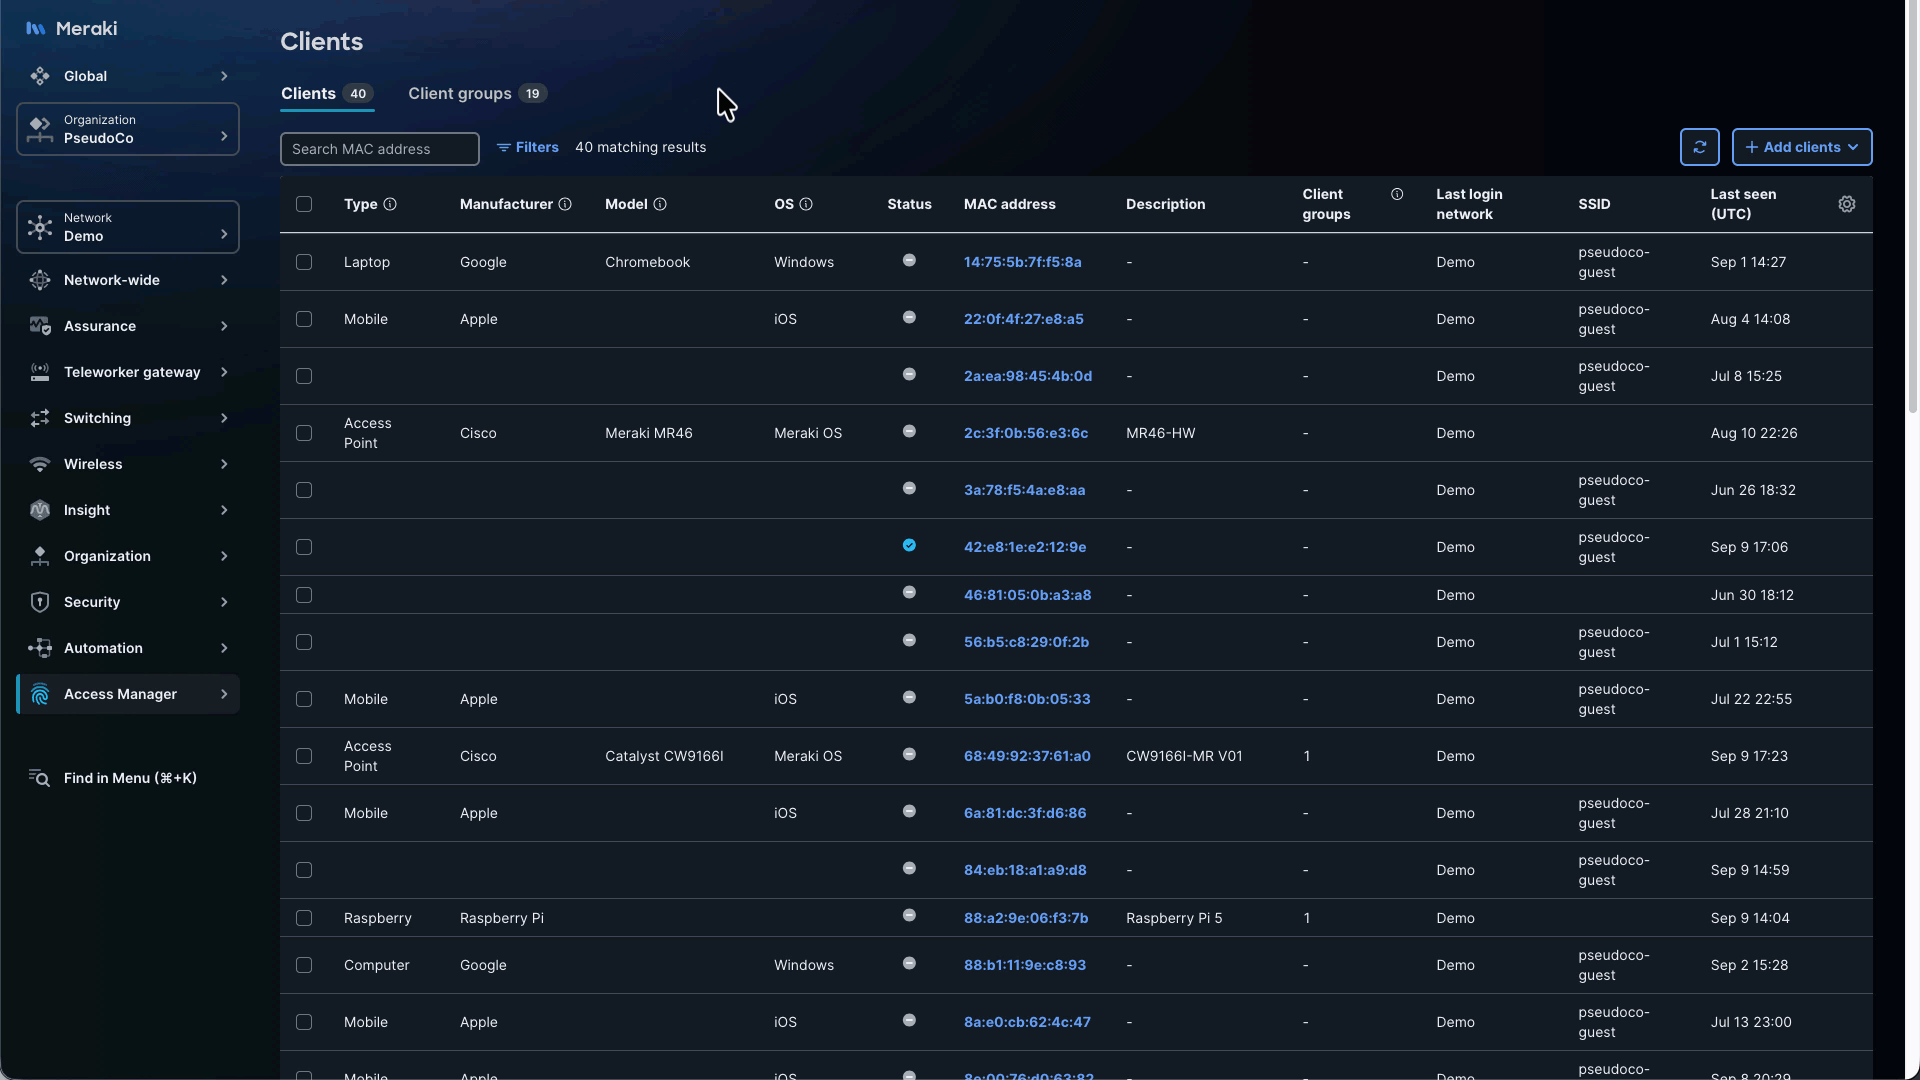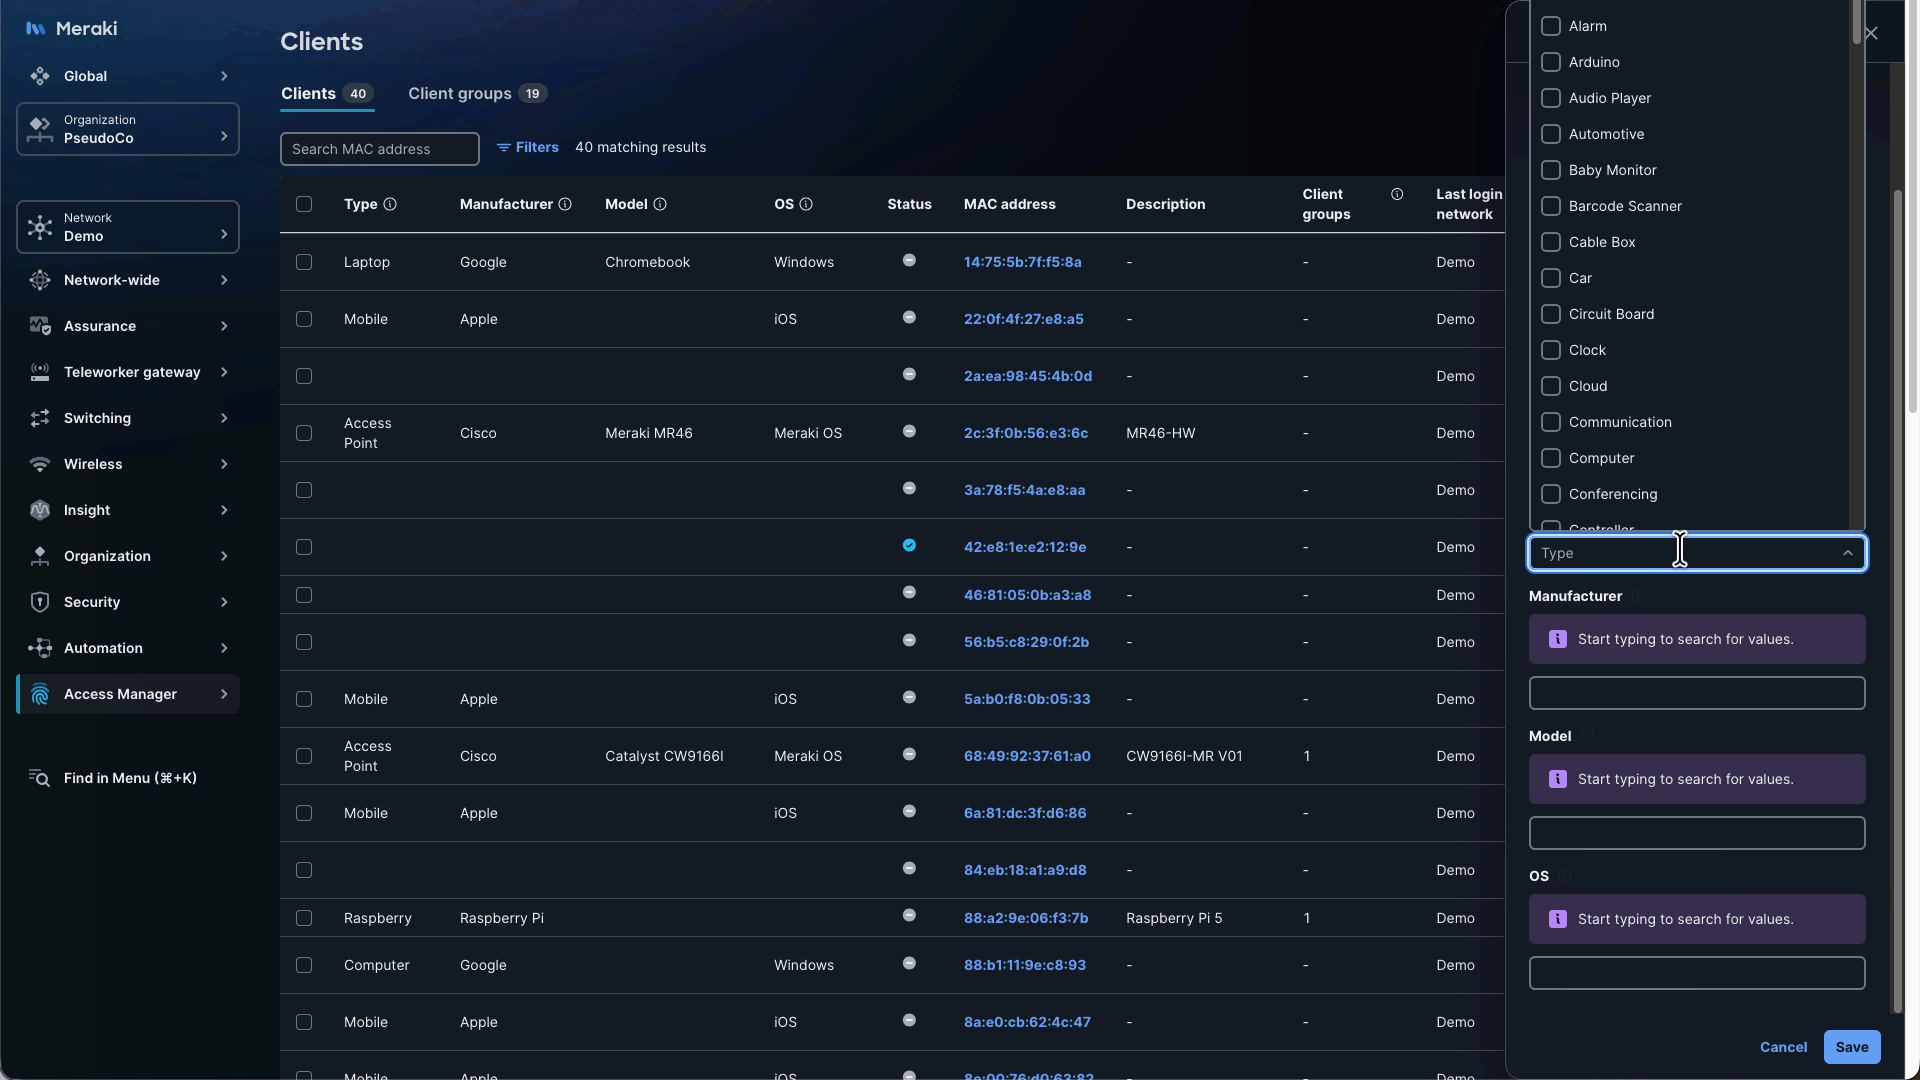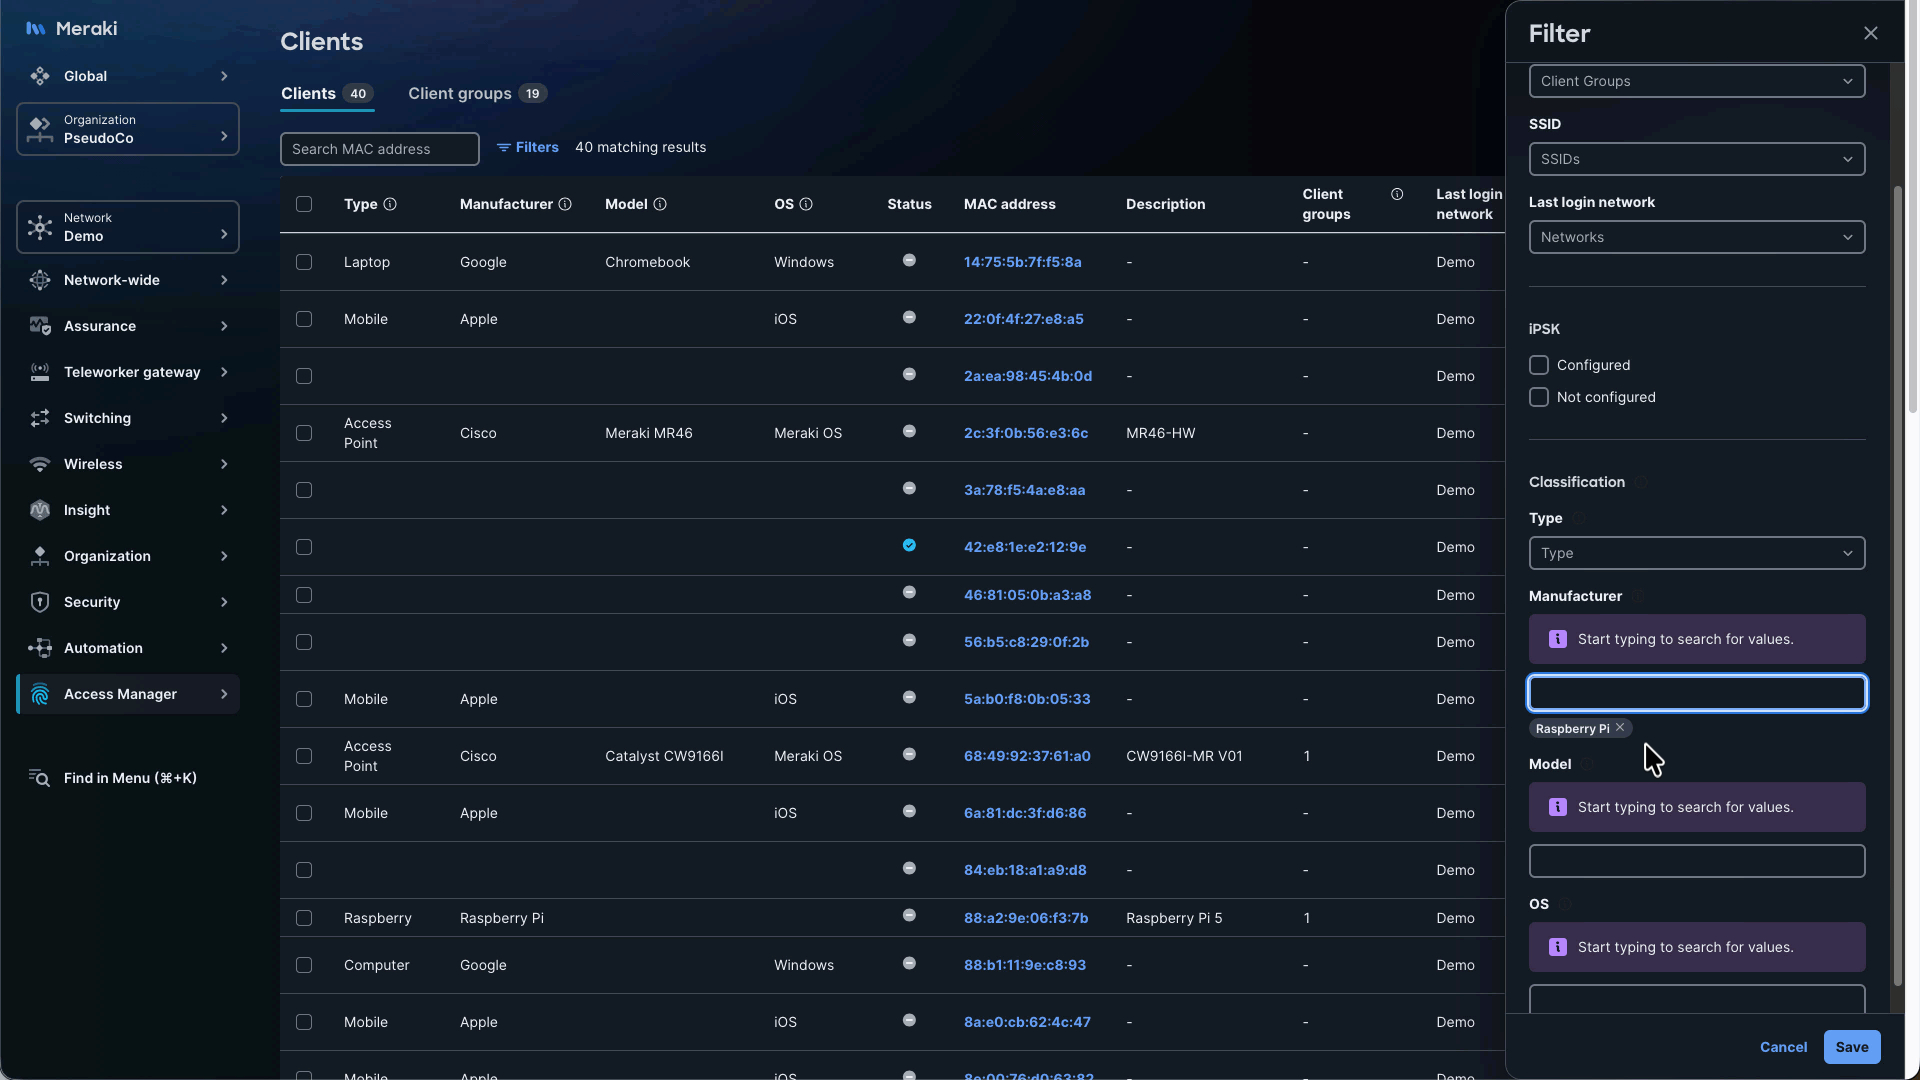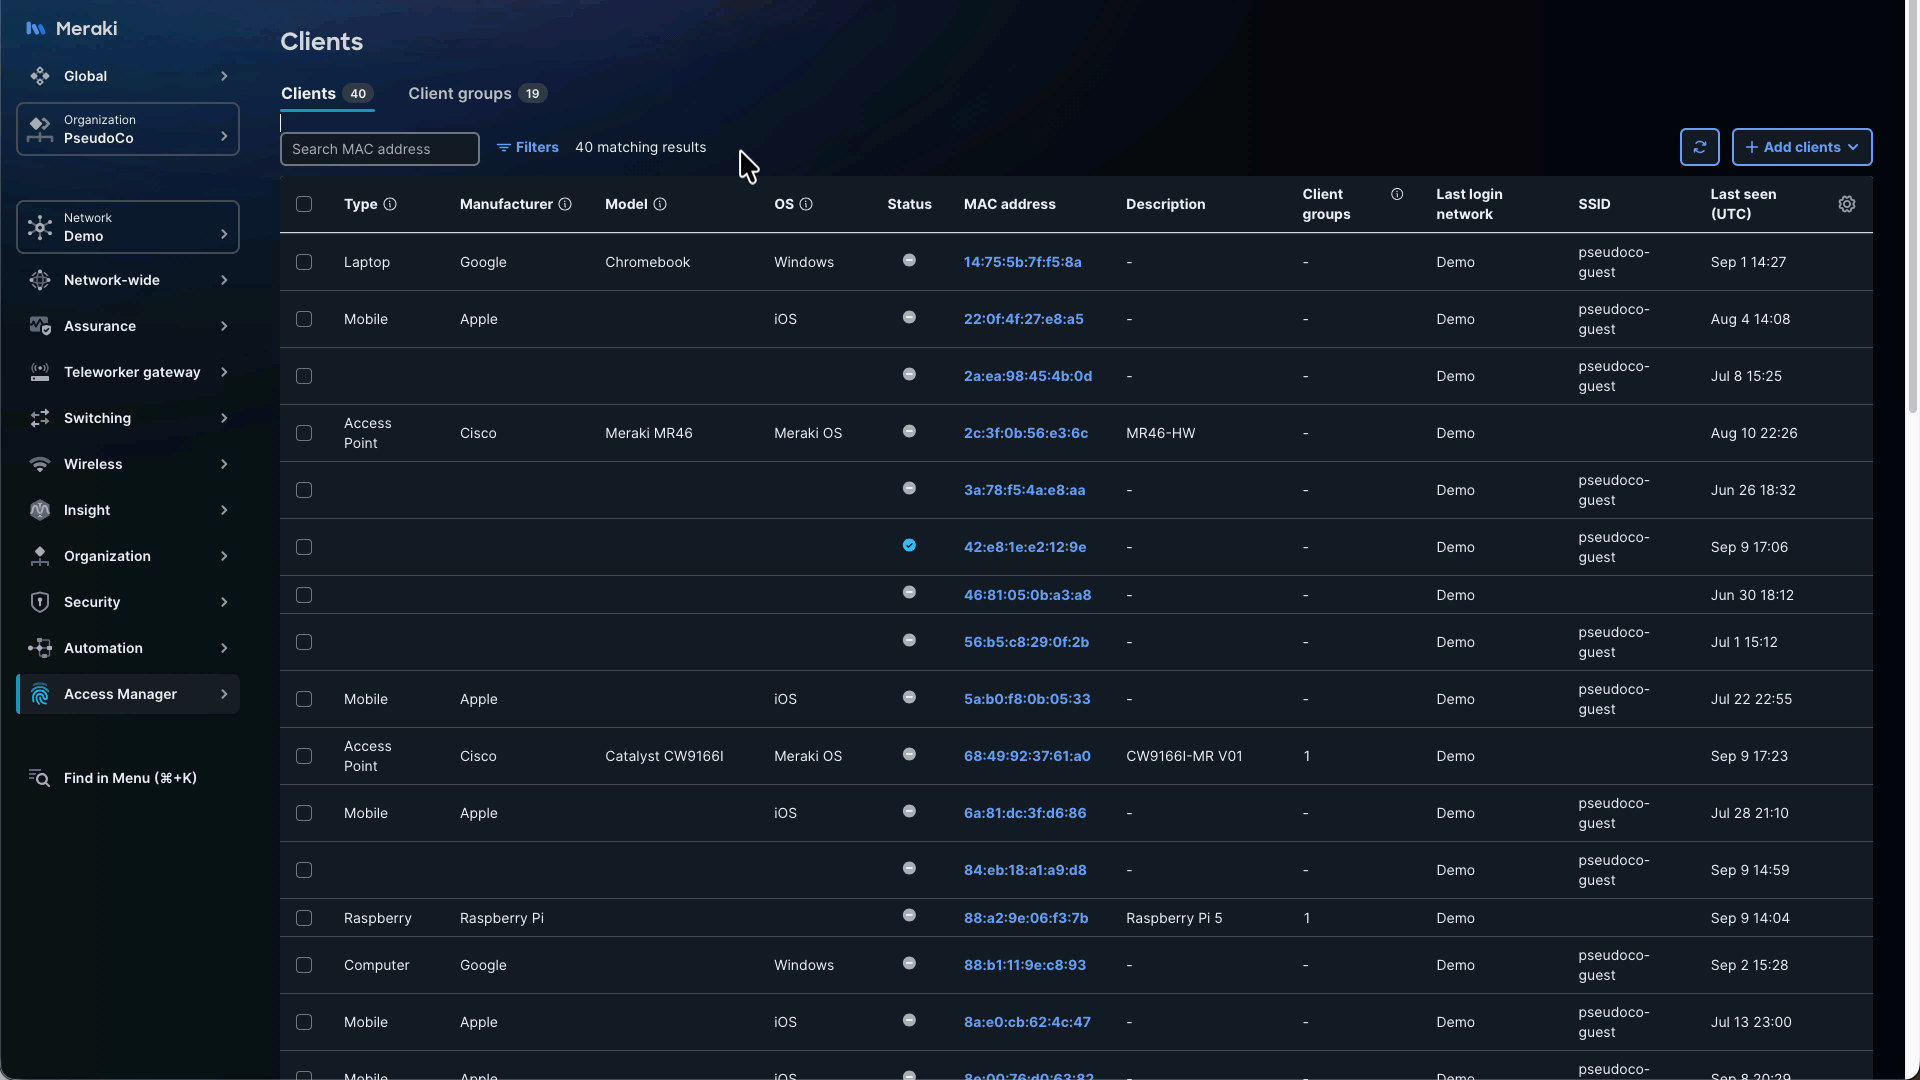
You may then use these profiling labels in your Access Rules with the Endpoints attribute source to match your clients' manufacturer, type, model, or OS values to simplify the authorization of your many endpoints! See Access Manager > Access Rules for examples.
Guest VLAN Support
2026-04-07
Guest VLAN is a supported option under Switching > Configure > Access Policies.
Cisco Access Manager General Availability
2025-11-10
Cisco Access Manager is now Generally Available!
- Authentication:
- 802.1X with EAP-TLS Certificate Based Authentication (optional Entra ID User Lookup)
- 802.1X with EAP-TTLS/PAP Username+Password Authentication with Entra ID
- MAC Authentication Bypass (MAB) for wired I/OT clients
- Identity Pre-shared Key (iPSK) per Authorization Rule for wireless I/OT clients
- Authorization Options: VLANs, Voice Domain, Adaptive Policy (SGTs) , iPSK, Group Policies
- Identity Providers: Microsoft Entra ID
- Supported Devices: All Cisco MS Switches, Cloud Configured Catalyst switches, MR APs and Cisco Wireless (CW) APs