
Cisco Campus Gateway Data Plane Encryption Configuration Guide
Overview and Purpose
While Cisco Campus Gateway (CG) supports deployment within a large campus network, some deployments place the Campus Gateway in a central location, such as a data center, to serve a large geographic area. In these deployments, the connection from the access points (APs) to the Campus Gateway may traverse untrusted links, such as direct internet access, rather than a site-to-site VPN. Virtual Extensible LAN (VXLAN) tunnel encryption for the data plane tunnels between the Campus Gateway and APs is essential in these environments.
Starting with MCG 32.2 and MR 32.2, CG supports encryption of the VXLAN data plane tunnels between the Campus Gateway and access points. After upgrading to this firmware version or later, the Campus Gateway always encrypts the VXLAN management traffic, including Bidirectional Forwarding Detection (BFD) keepalives, RADIUS, and MR Neighbors, within the VXLAN tunnel. Client data traffic remains unencrypted by default unless you explicitly enable it.
VXLAN tunnel encryption uses Datagram Transport Layer Security (DTLS) 1.2 with AES-128-GCM. The Campus Gateway generates a pre-shared key (PSK) upon AP registration and secures the tunnel with this key. The Campus Gateway sends the PSK to the access point using the secured QUIC control plane tunnel in the Registration reply message.
When data plane encryption is enabled, the maximum packet size is 1412 bytes. Data plane encryption adds 38 bytes of overhead in addition to the 50 bytes of VXLAN overhead.
Prerequisites and Limitations
Before configuring Campus Gateway Data Plane Encryption, ensure the following requirements are met:
Licensing Requirements
|
License type |
Required license |
|
Co-Termination Licensing |
MR Enterprise |
|
Meraki Subscription Licensing |
MR Enterprise |
|
Cisco Networking Subscription |
Cisco Wireless Essentials |
Hardware Requirements
Campus Gateway data plane encryption is available on the following devices:
-
MR and CW access points: All Wi-Fi 6 or later models
-
Campus Gateway: All models
Firmware Requirements
Campus Gateway data plane encryption requires the following firmware versions:
-
MR and CW access points: MR 32.2.3 or later
-
Campus Gateway: MCG 32.2.3 or later
Limitations
- Enabling data plane encryption requires the access points to rejoin the Campus Gateway. Wireless network operations are disrupted during this process. Enable this feature during a maintenance window.
- When data plane encryption is enabled, maximum throughput for access points tunneling to the Campus Gateway decreases due to encryption overhead.
Configuration Steps
Enable data plane encryption
-
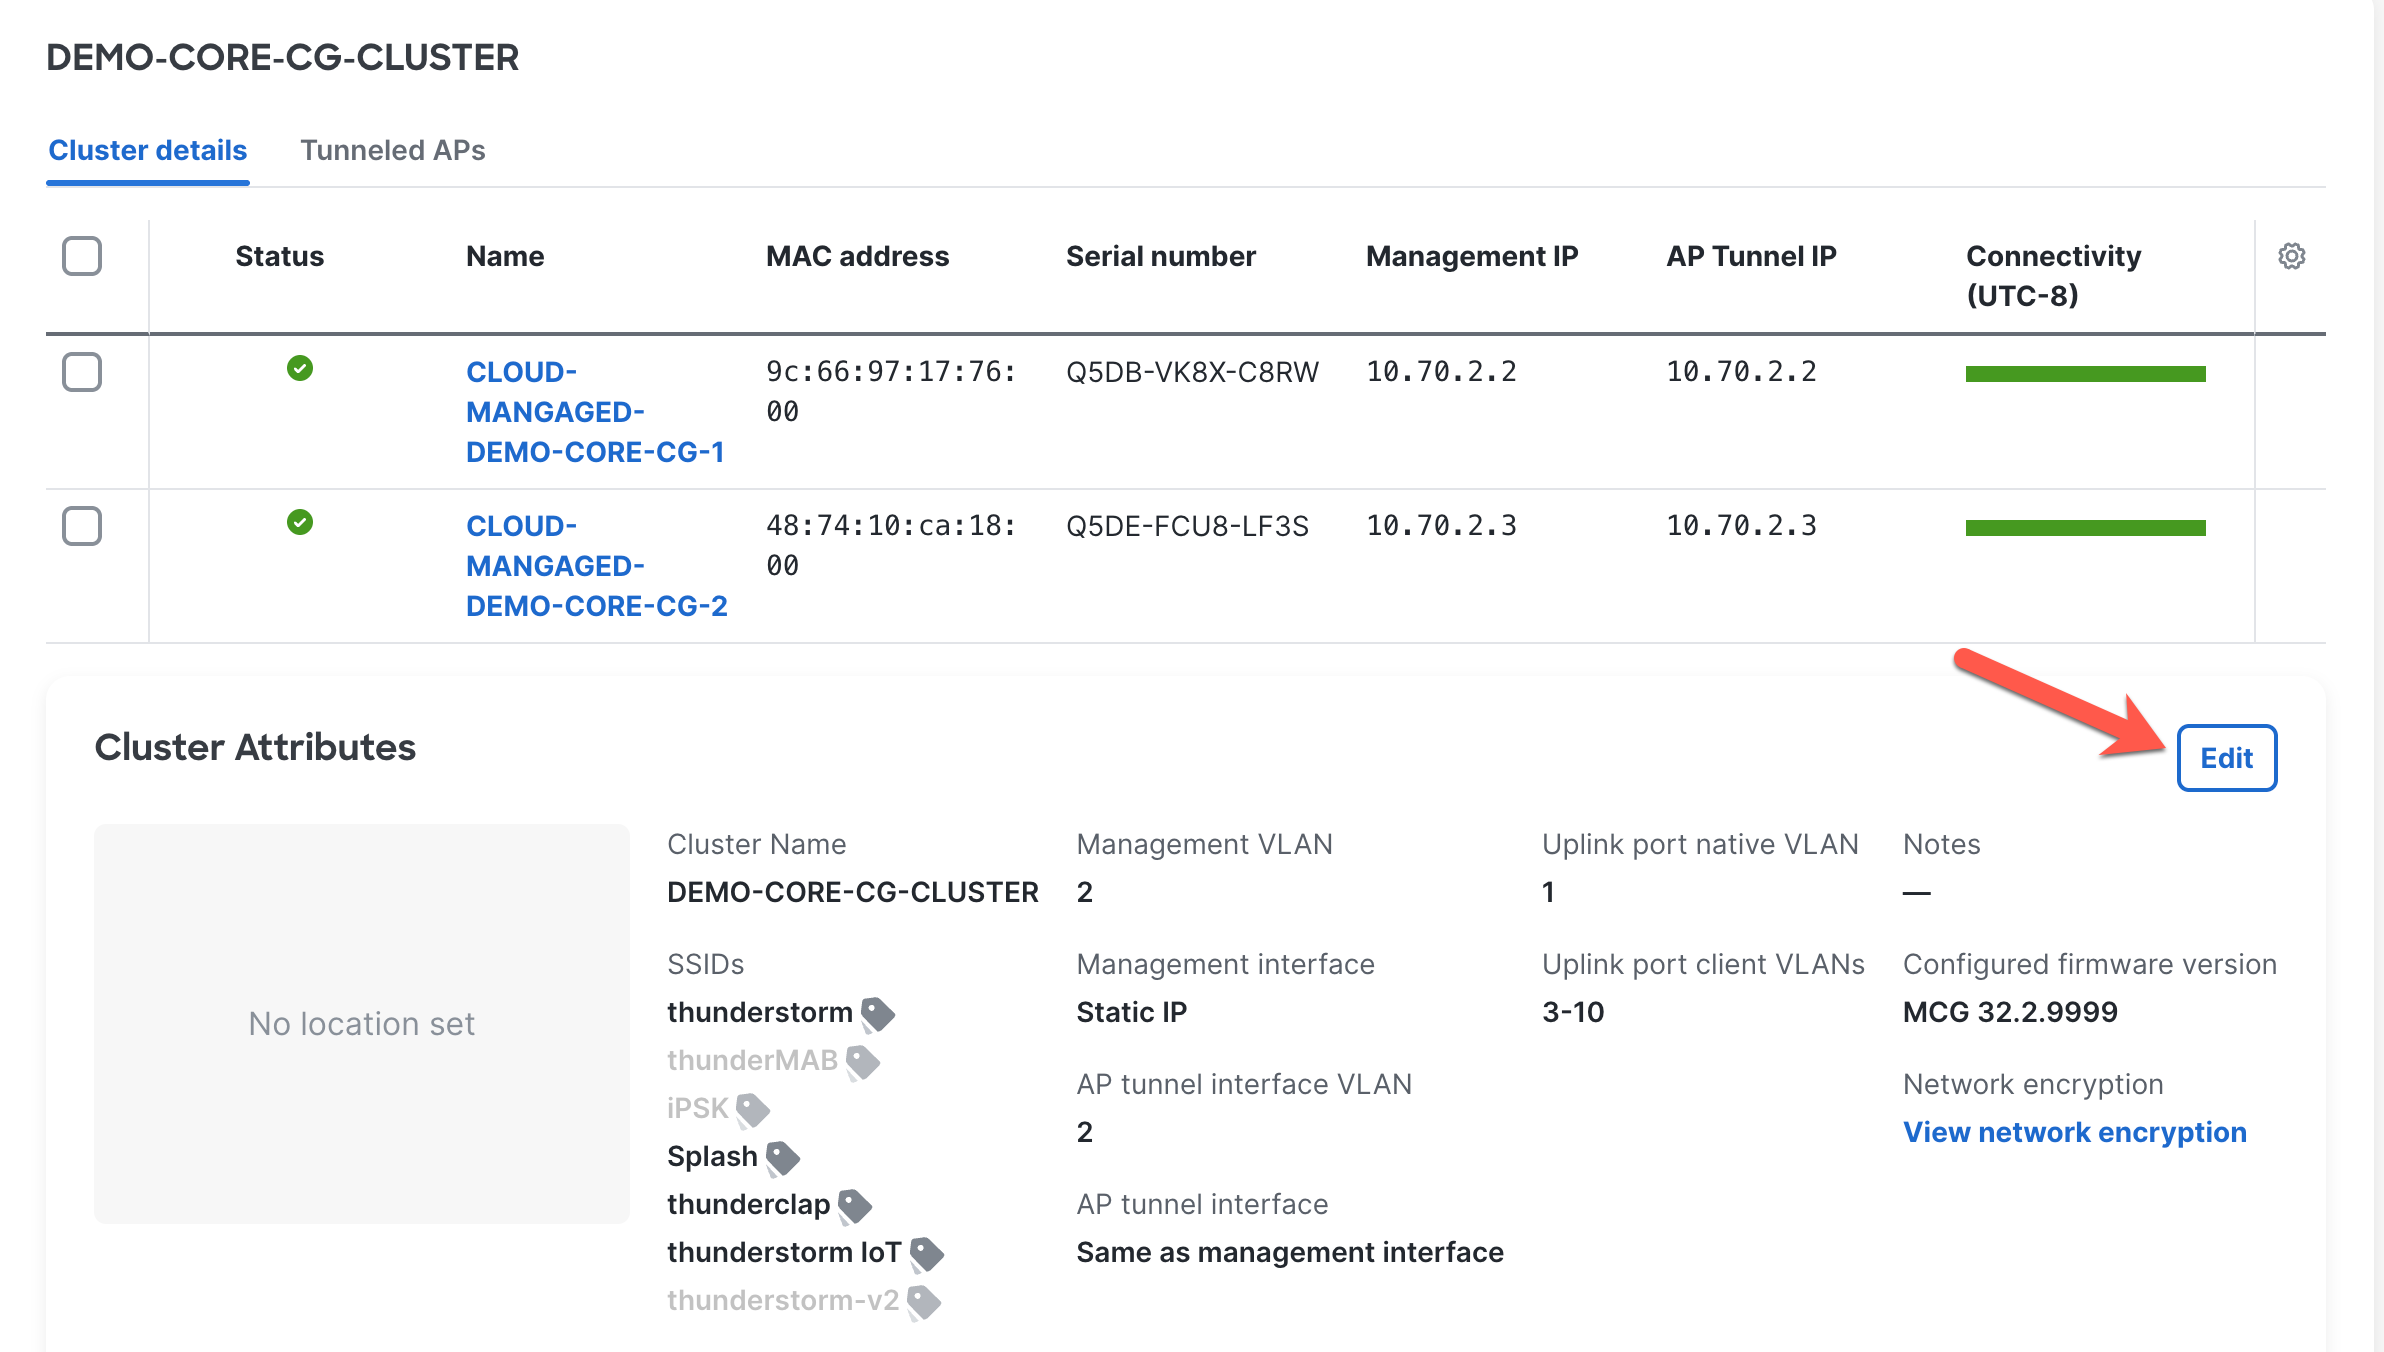
Navigate to Wireless > Campus Gateway > Campus Gateways.
-
Choose Edit to open the Edit cluster attributes dialogue box.
-
In the Data traffic encryption enabled on networks field, choose the networks to enable encryption on.

-
Choose Save.
Note: The Campus Gateway and access points must reside in the same Meraki network. Only the Meraki network where the Campus Gateway resides is available for selection.
Verification
- To verify the networks with data plane encryption enabled, choose View network encryption on the cluster overview page.

- To check the encryption status of each access point, navigate to the Tunneled APs tab and view the Encryption status column. An Encrypted status appears next to each access point.
